AI Agents SDLC Platform: Authoring, Enforcement, and Documentation Agents Across the Full Software Development Lifecycle
The AI agents SDLC
platform.
Three classes of AI agents across the full SDLC. Authoring agents draft user stories and test plans for human review. Enforcement agents verify the SDLC was followed. Documentation agents continuously produce release artifacts and audit-ready evidence packages. Five shipped integrations. Authoring and documentation agents shipping today; 6 PR gates run by Code Sentinel and 6 release gates run by Release Gatekeeper.
Three minutes on the gap between the process you wrote down and the one your team actually ran. The screens shown are product designs, not a live recording.
Monday morning, 9:14 AM.
Sarah opens SDLC Playbook to see what happened across her four squads over the weekend. The Accountability Score answers her board’s question before her coffee is done.
She drills into the squad that dropped 12 points last week. The Root Cause Analysis explains why in two sentences. One Slack message later, the conversation is on the calendar.
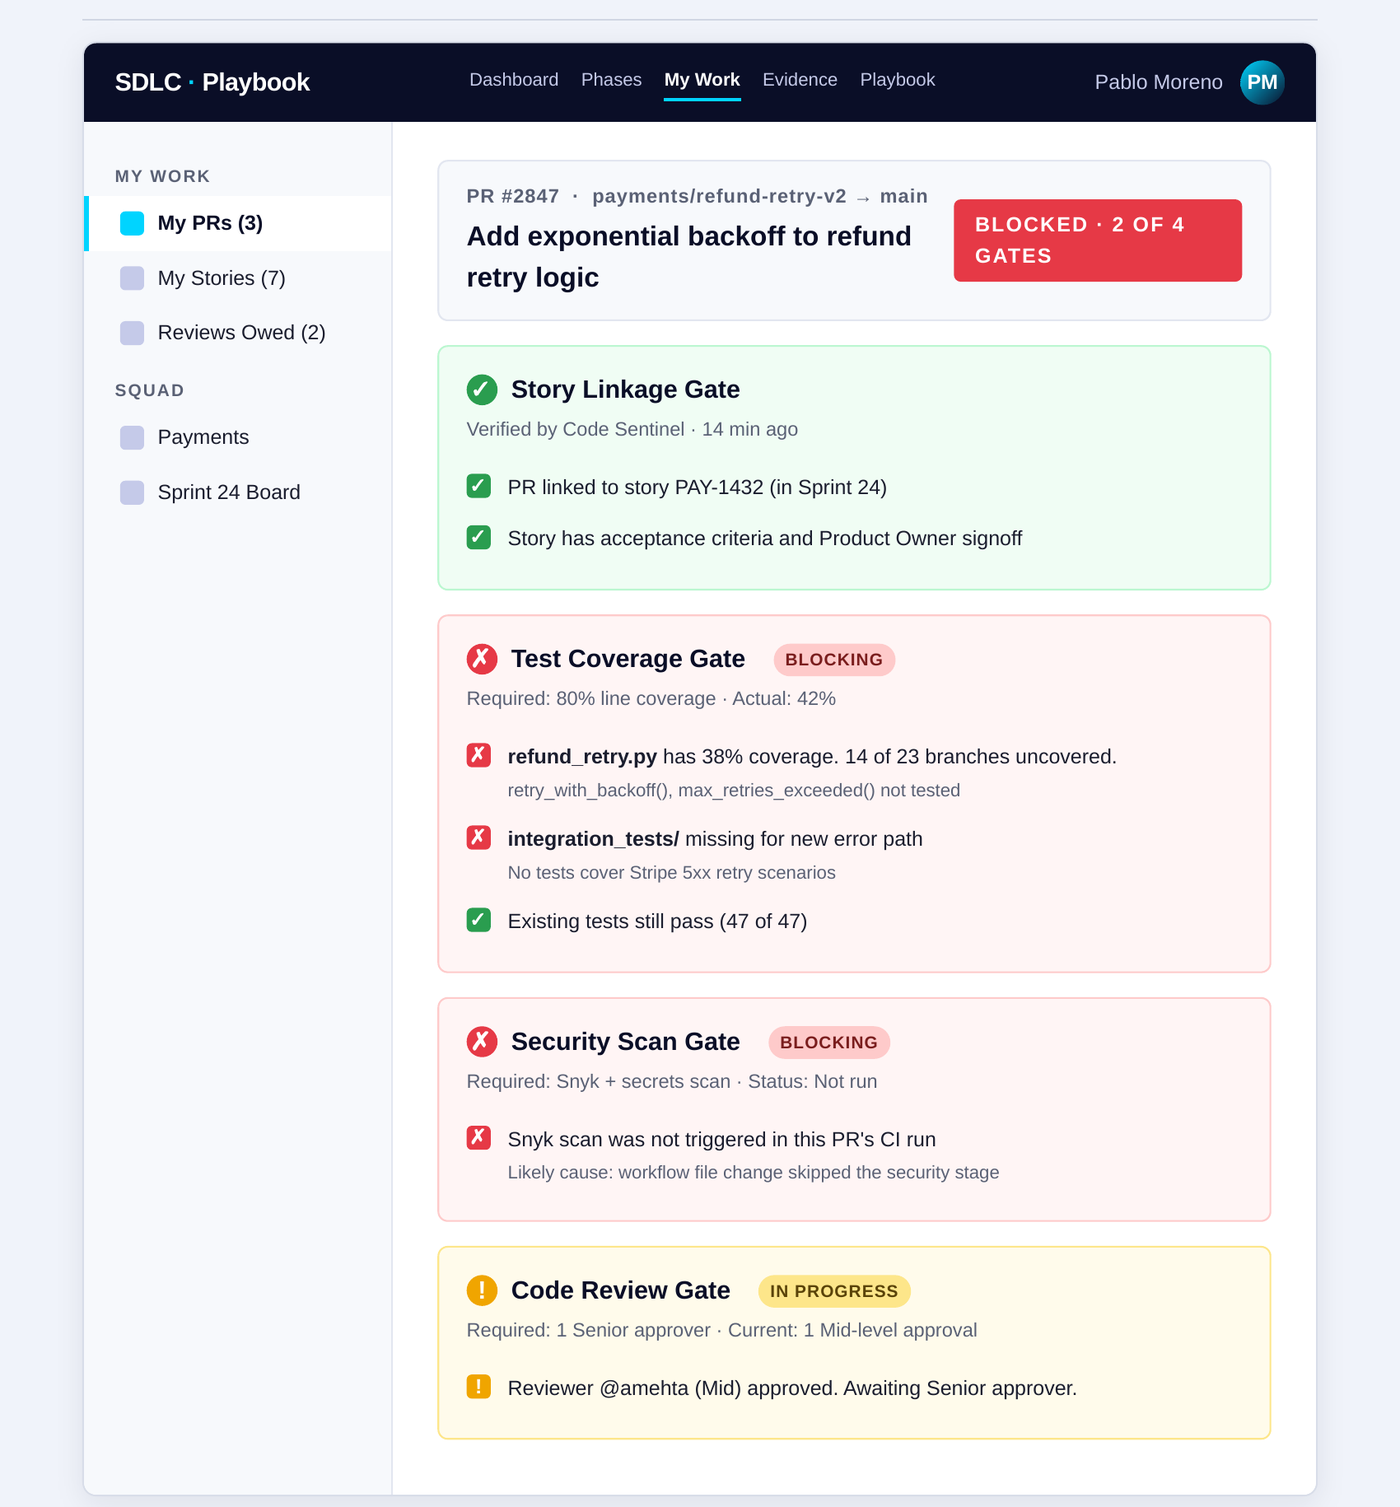
The merge that won’t go through.
Pablo expects his PR to land in 30 minutes. Code Sentinel blocks it. But instead of a red CI badge and a 400-line log, he sees four named gates with the exact reason each one passed or failed.
The Coach explains the fixes in his language. Then it offers to draft the missing test cases. He clicks once. Six tests appear in a sub-PR. He merges and moves on.
The story that writes itself.
Maya has six new feature requests from customer success and a sprint planning meeting in two hours. She types two sentences into Requirements Author. The agent drafts the user story with proper acceptance criteria, identifies missing NFRs, and suggests a story split.
Side-by-side review. AI draft on the left, her edits on the right. She accepts three sections, regenerates one with feedback, edits the last. One click, the story lands in Jira with a full authorship audit trail. Thirty minutes of writing becomes five minutes of editing.
I want to push evidence packages to ServiceNow
So that change tickets reference the SDLC trail
+ 2 NFRs flagged missing
+ Suggested story split
The test plan that writes itself.
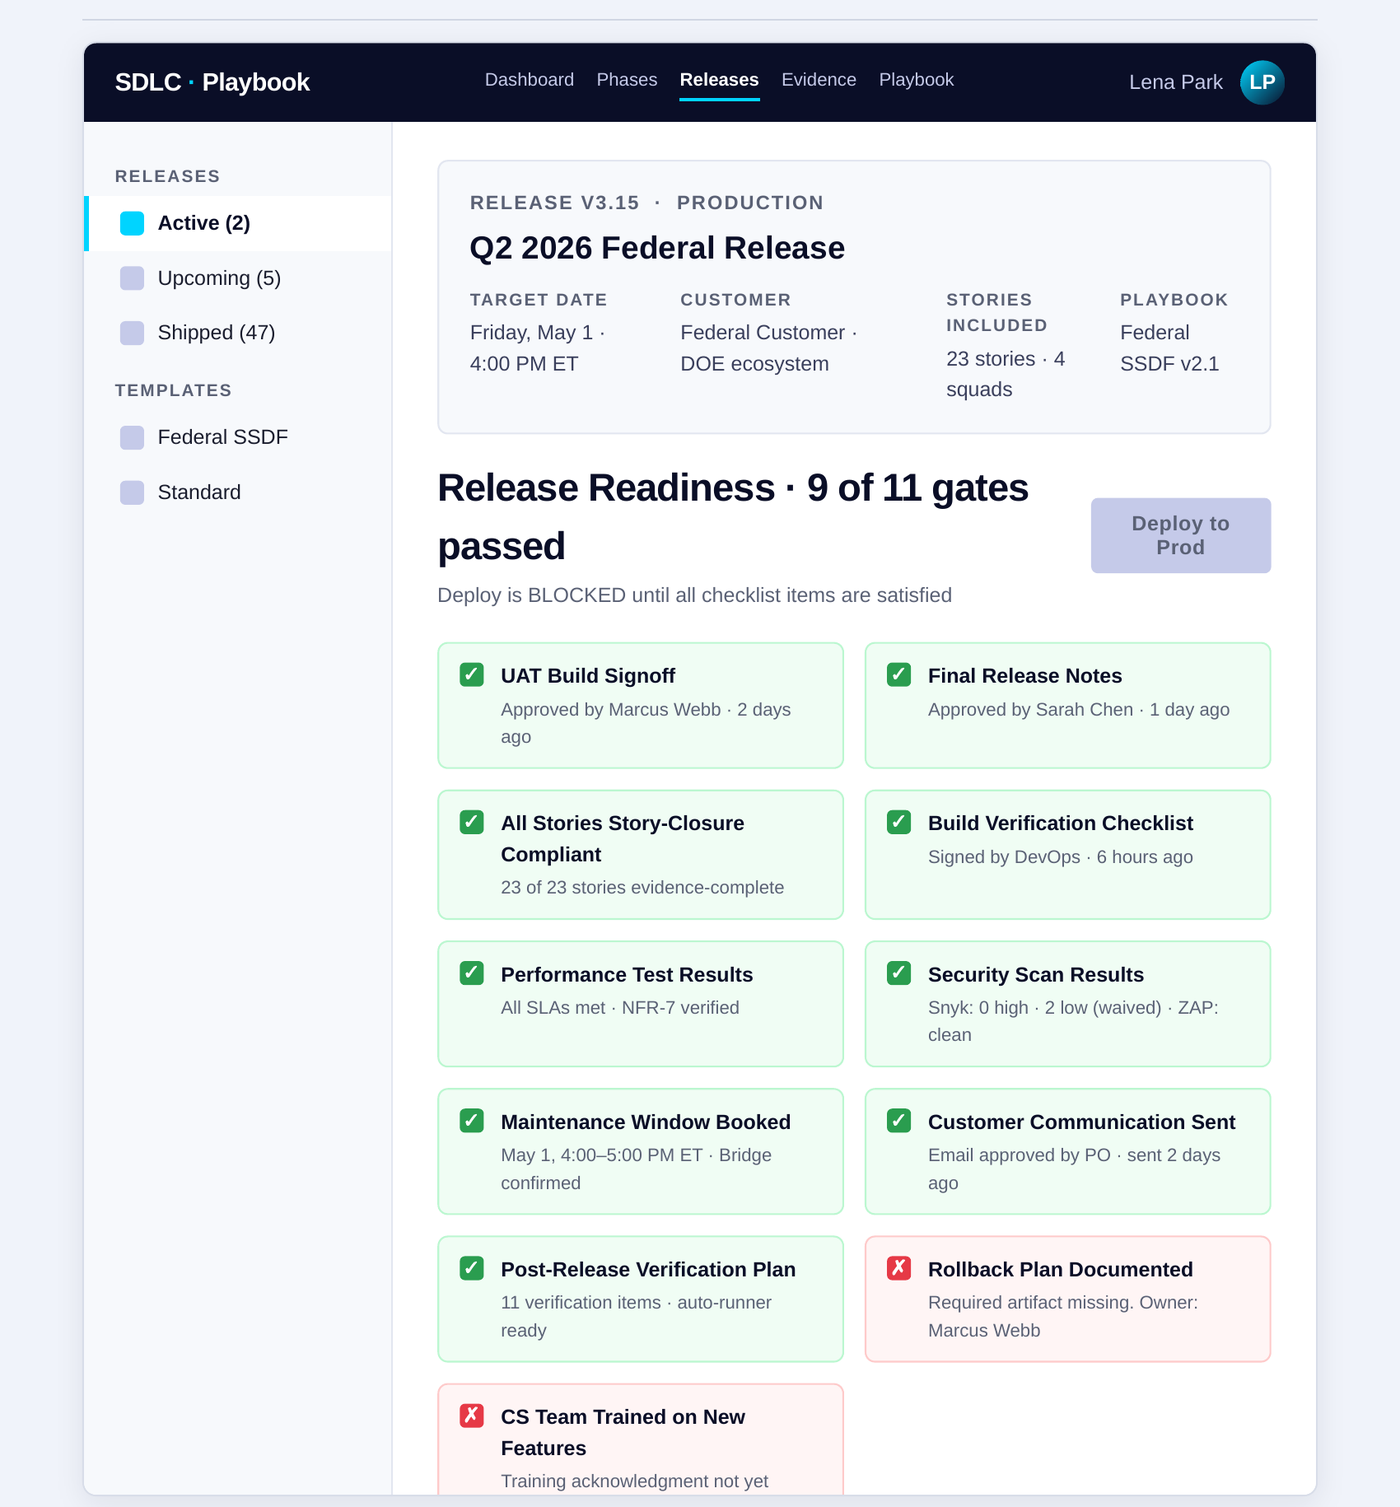
Lena opens the new story in Jira. QA Strategist has already drafted the test plan: test cases for each acceptance criterion, edge cases, UAT scripts, and the test data that will be needed. She reviews, adjusts two cases, accepts the plan.
Two days later the release with that story is ready. Nine of eleven gates passed. The Deploy button is greyed out because the rollback plan is missing. No amount of pressure changes that. Once both items resolve, she clicks Deploy. Audit-ready, signed, sealed.
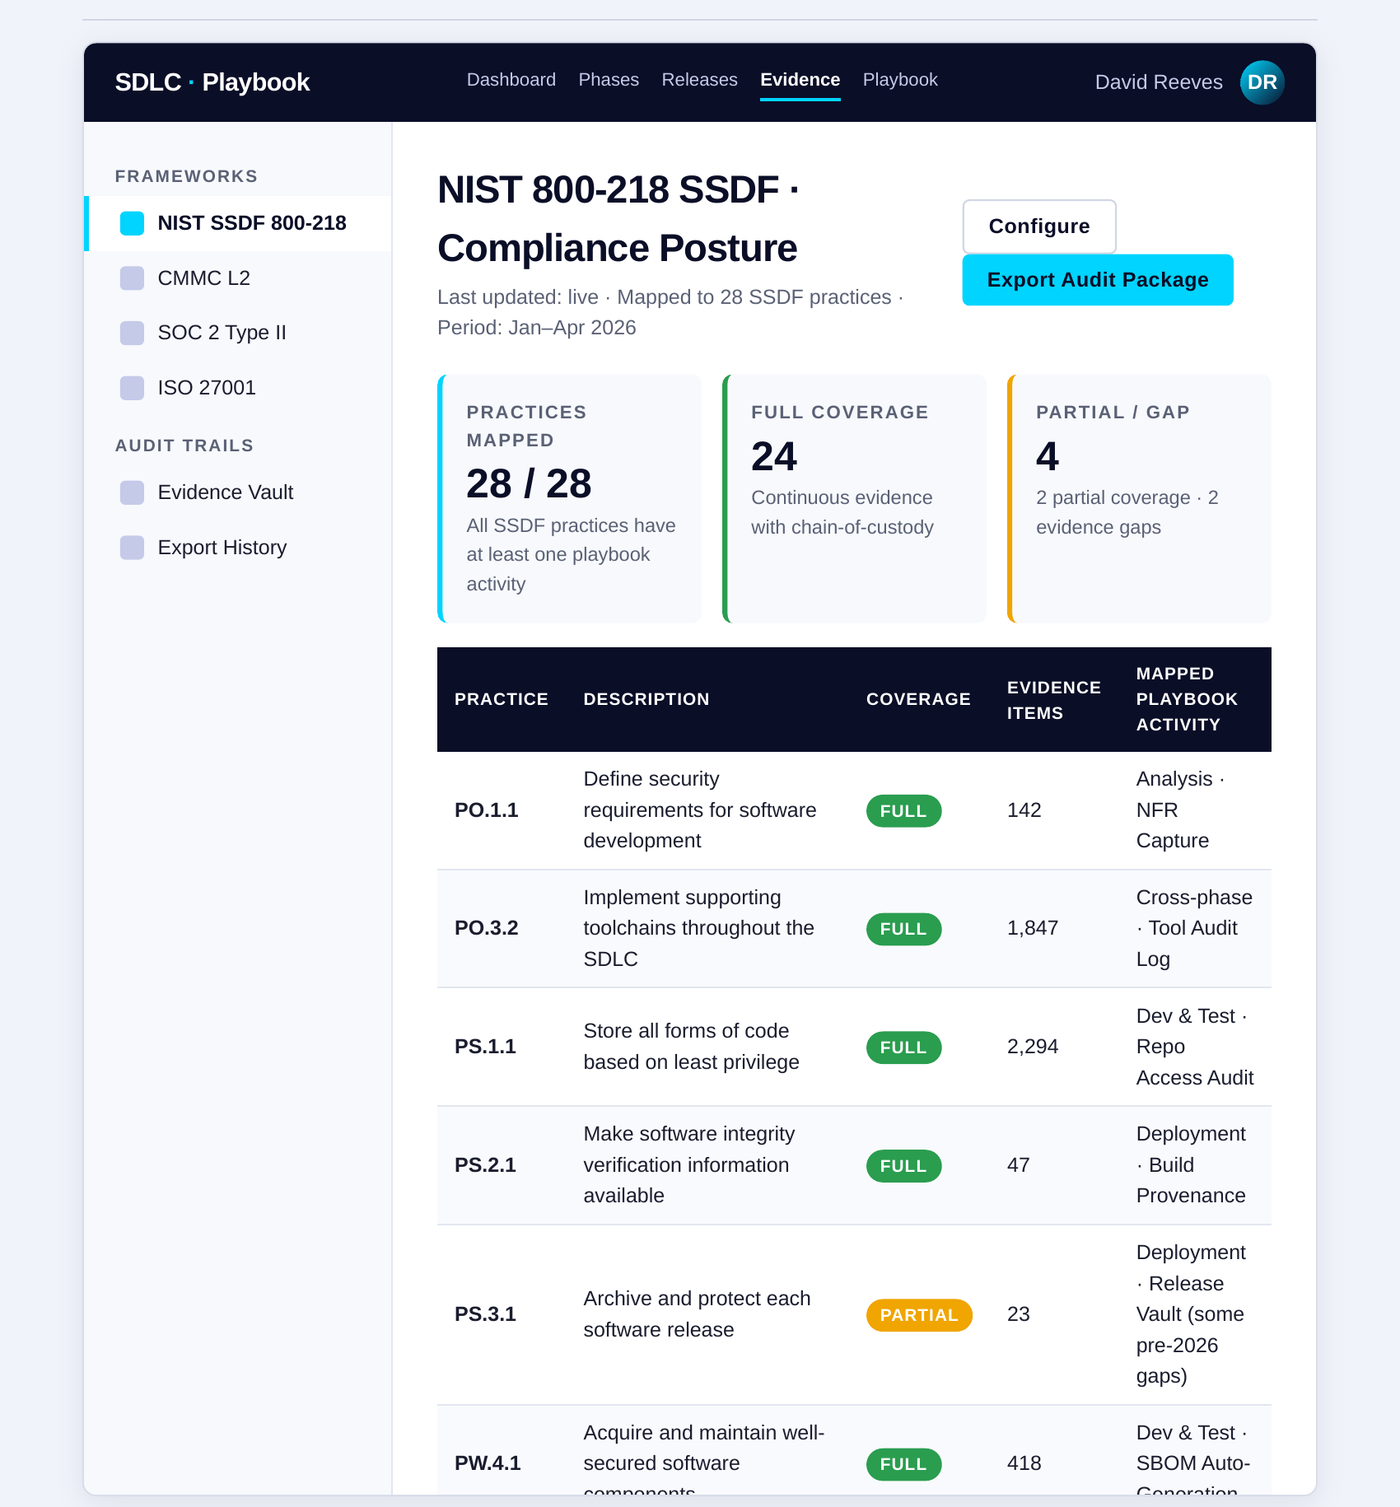
The auditor shows up unannounced.
David needs evidence for the company’s compliance posture — SOC 2, NIST 800-218 SSDF, or NIST 800-171, whichever framework is in scope. The Evidence Vault shows controls mapped, with the two minor gaps already flagged in the compliance posture view before the auditor finds them.
One click. Signed PDF, evidence ZIP, chain-of-custody manifest. Tamper-evident. Evidence-gathering stops being a reconstruction exercise: the package is retrieved from the vault, not rebuilt from chat threads and memory, with the authorship trail showing what was AI-drafted versus human-authored.
The offshore QBR that lands.
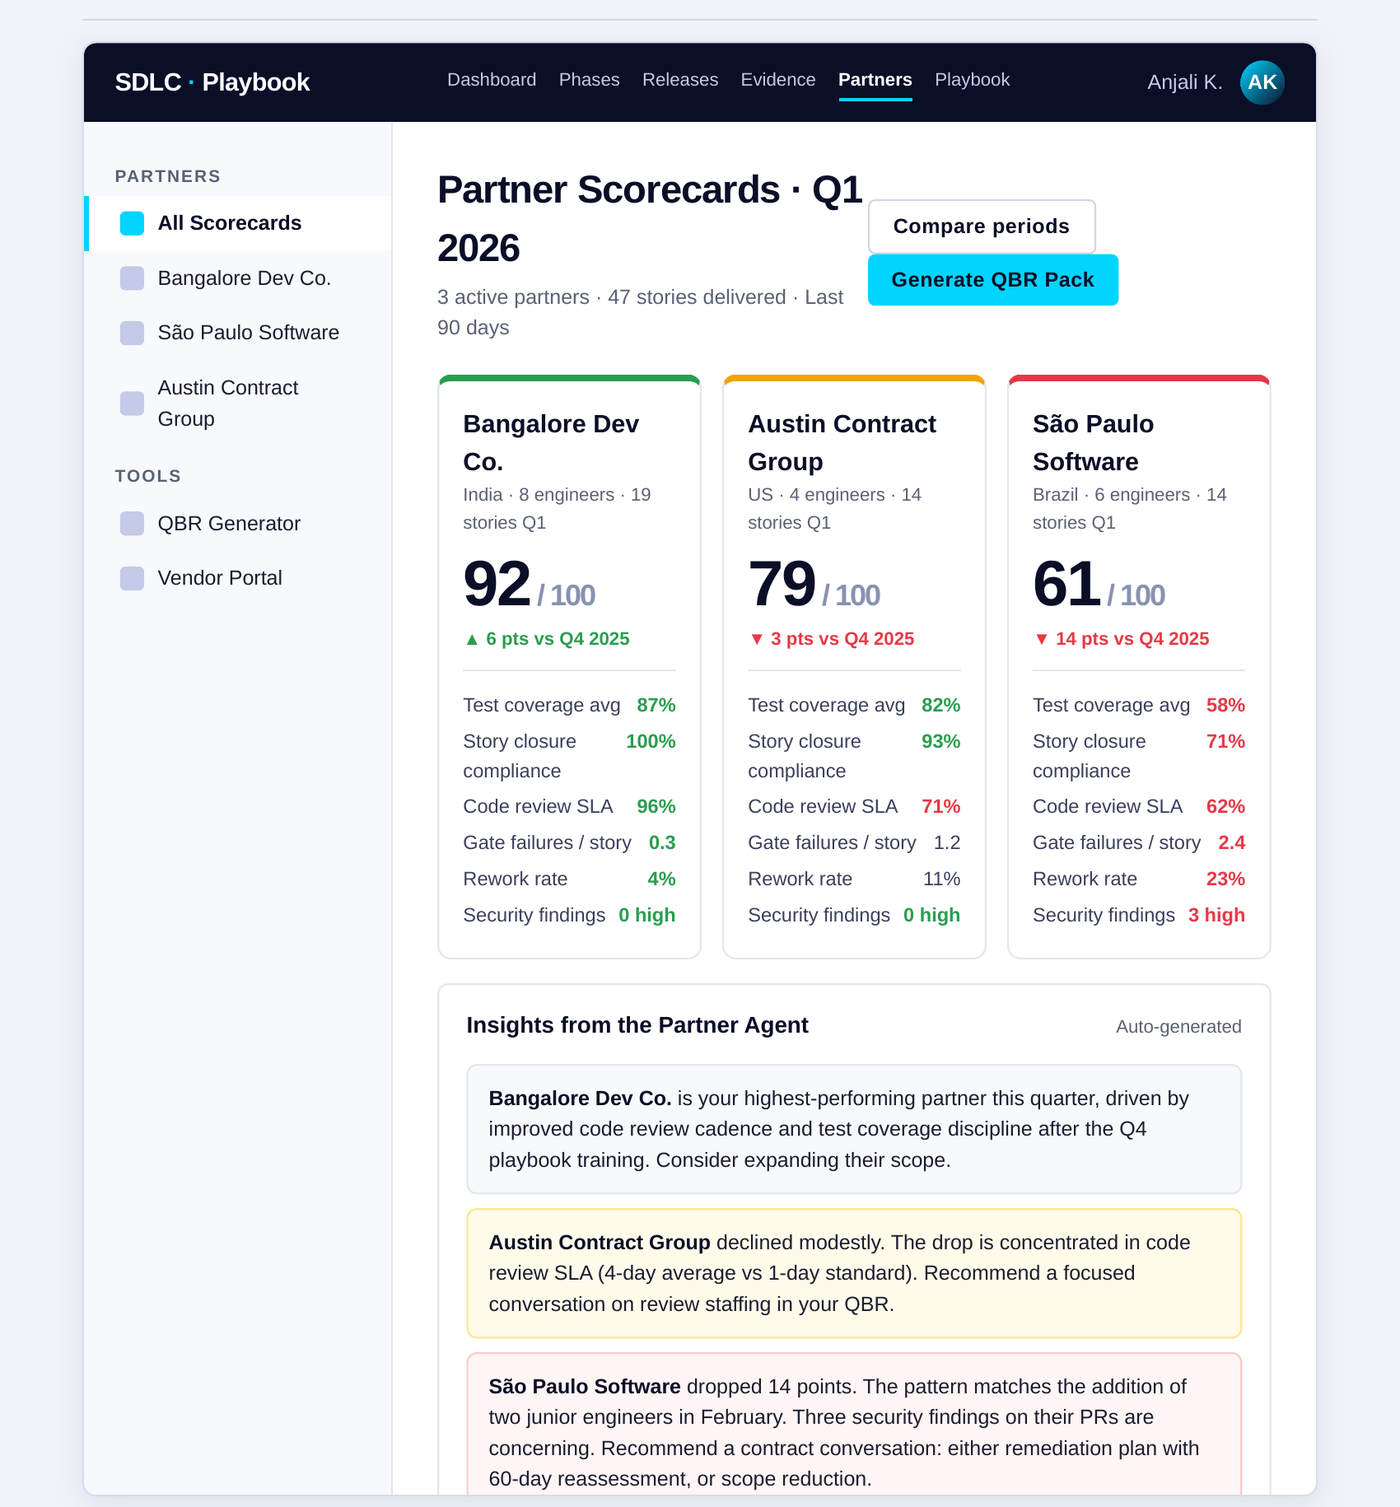
Anjali walks into the quarterly business review with three offshore partners. Three Partner Scorecards side by side, ranked by objective playbook adherence. Six metrics each. AI-generated talking points.
The conversation is no longer about vendor relationships. It is about specific metrics, specific engineers, and a clear renewal decision framework. Hard data wins every time.
The documents the
SDLC produces.
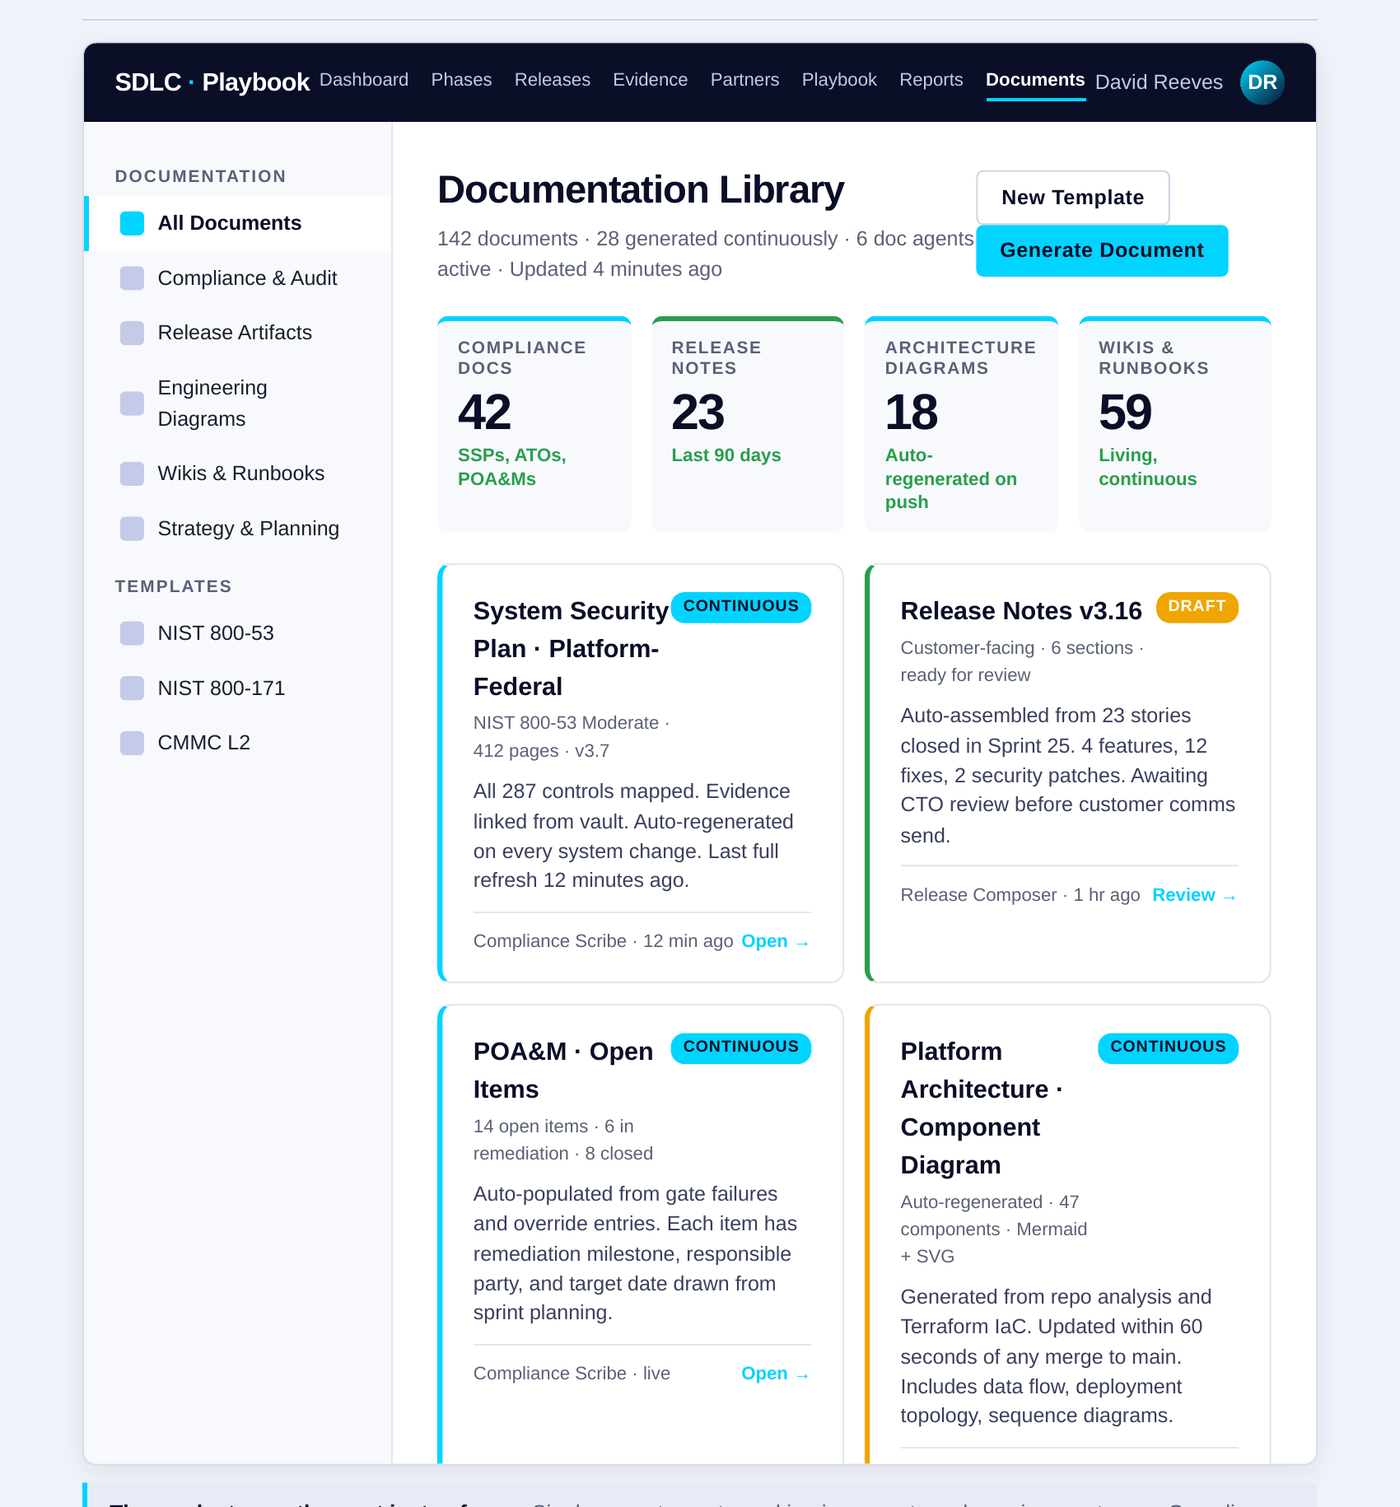
David needs the audit package — SOC 2 Type II, an SSDF assessment, or a federal SSP for a regulated contract. Compliance Scribe has been generating it continuously against the live evidence vault. Every claim cited. Every citation links back to specific evidence.
Signed and ready to ship. The compliance documentation is a byproduct of work moving through the SDLC, not a project assembled before the audit, and every claim in it can be followed to the evidence item it cites, so it survives the follow-up question.
A guided tour through
the working product.
Six more screens that show how the product handles the full SDLC, from the auditor walk-in to the board briefing.
One-click audit export
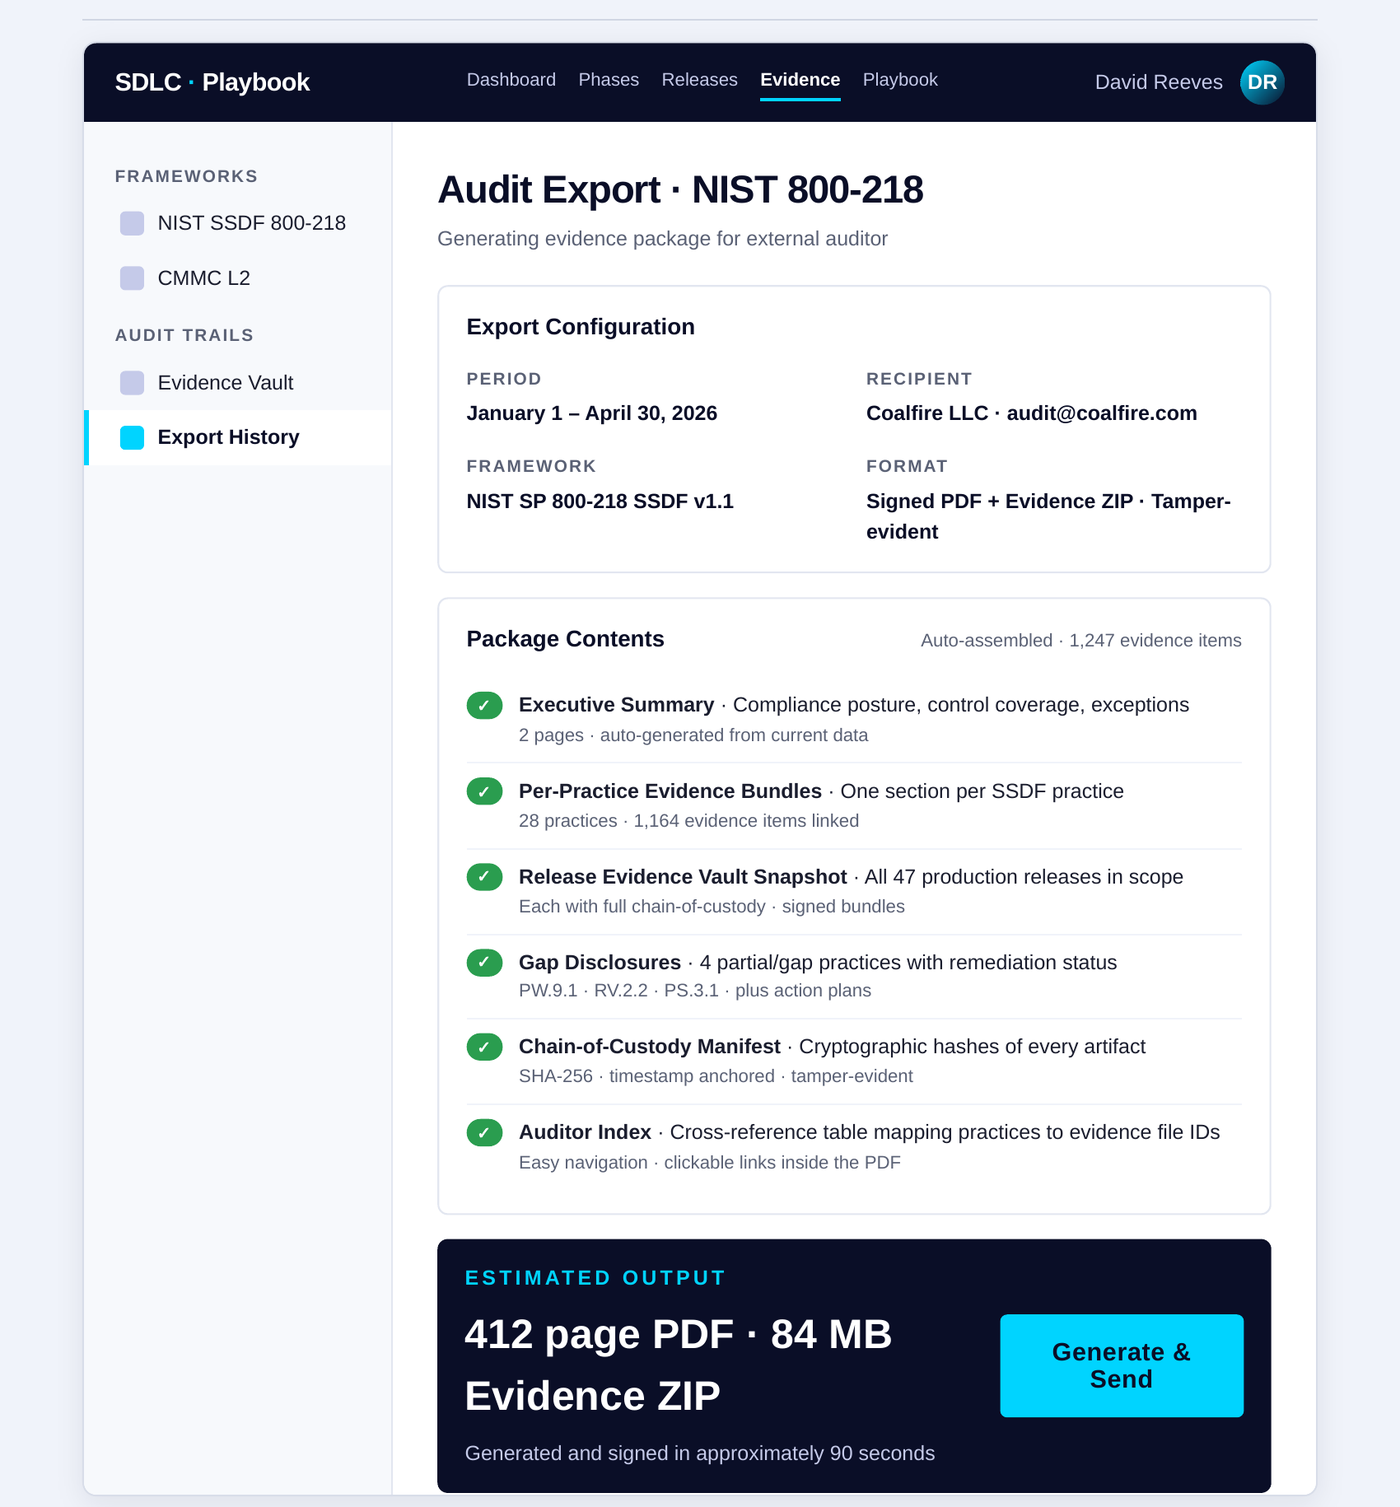
Signed PDF and evidence ZIP, tamper-evident, exported on demand for the period you name. Per-practice evidence bundles with chain-of-custody manifest. Coverage Statement distinguishes AI-authored from human-authored content.
Phase-by-phase workspace
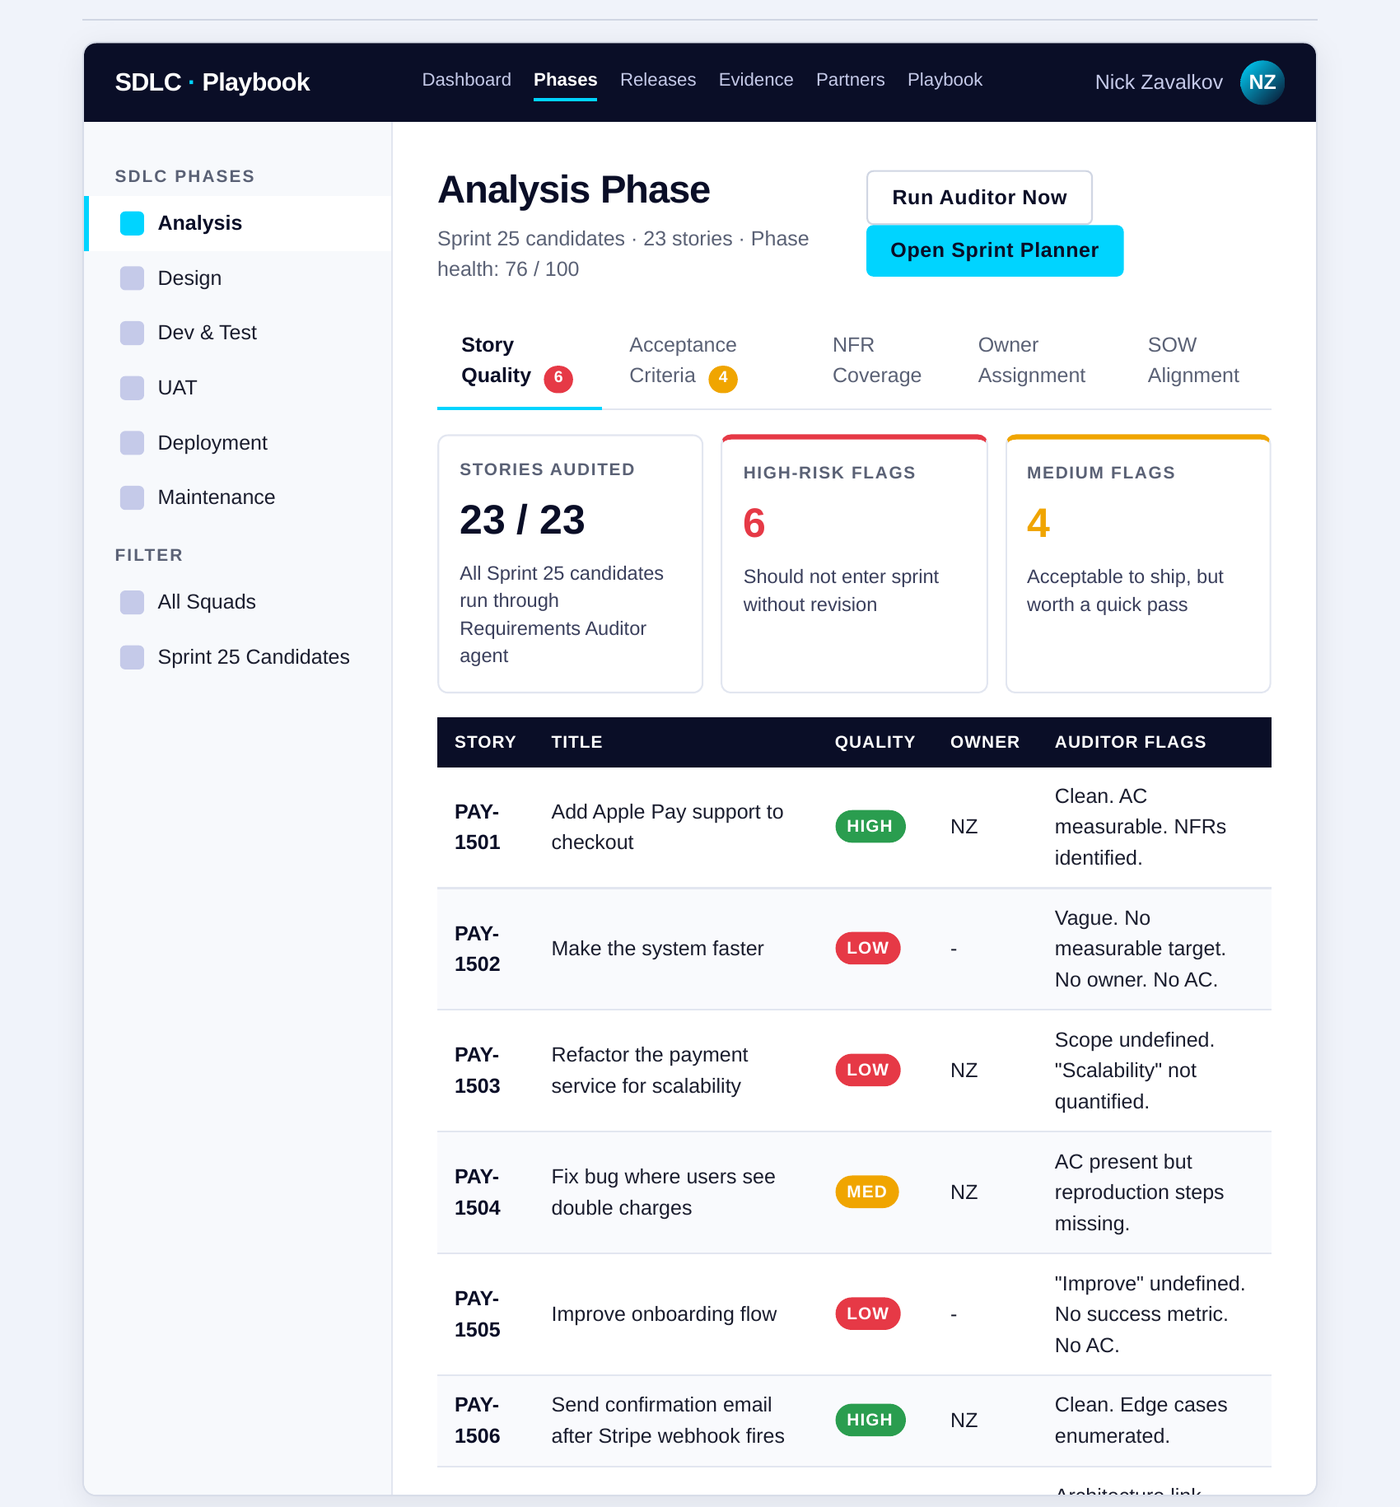
Each SDLC phase has its own dedicated view. Analysis, Design, Dev & Test, UAT, Deployment, Maintenance, all visible at story level. Methodology-aware: same product, different vocabulary for Scrum, Kanban, or Waterfall teams.
Reports for the board
Six high-leverage reports auto-assembled from the same evidence base. Board briefings, partner reviews, audit prep, all from one source of truth.
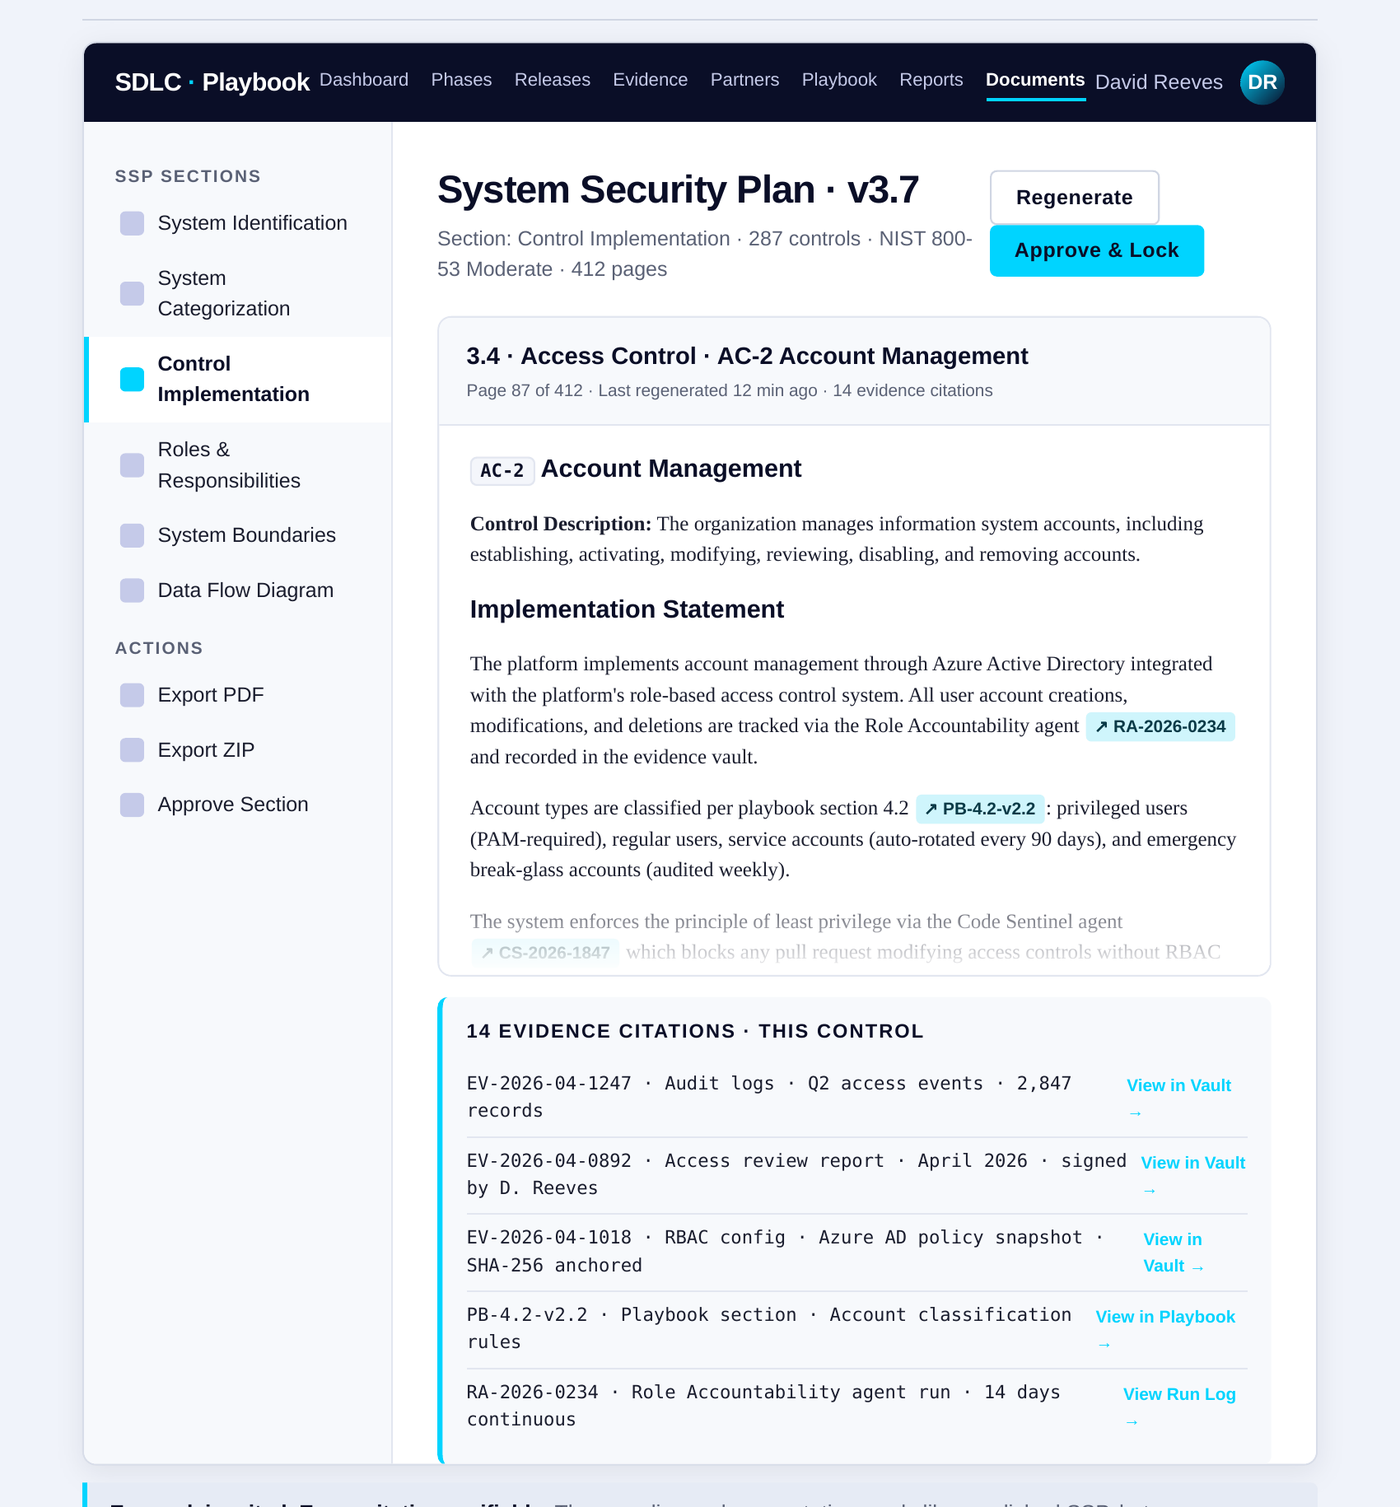
Every claim cited
SSPs read like polished compliance documents but every assertion links back to specific evidence in the vault. Auditors drill from prose to proof in one click.
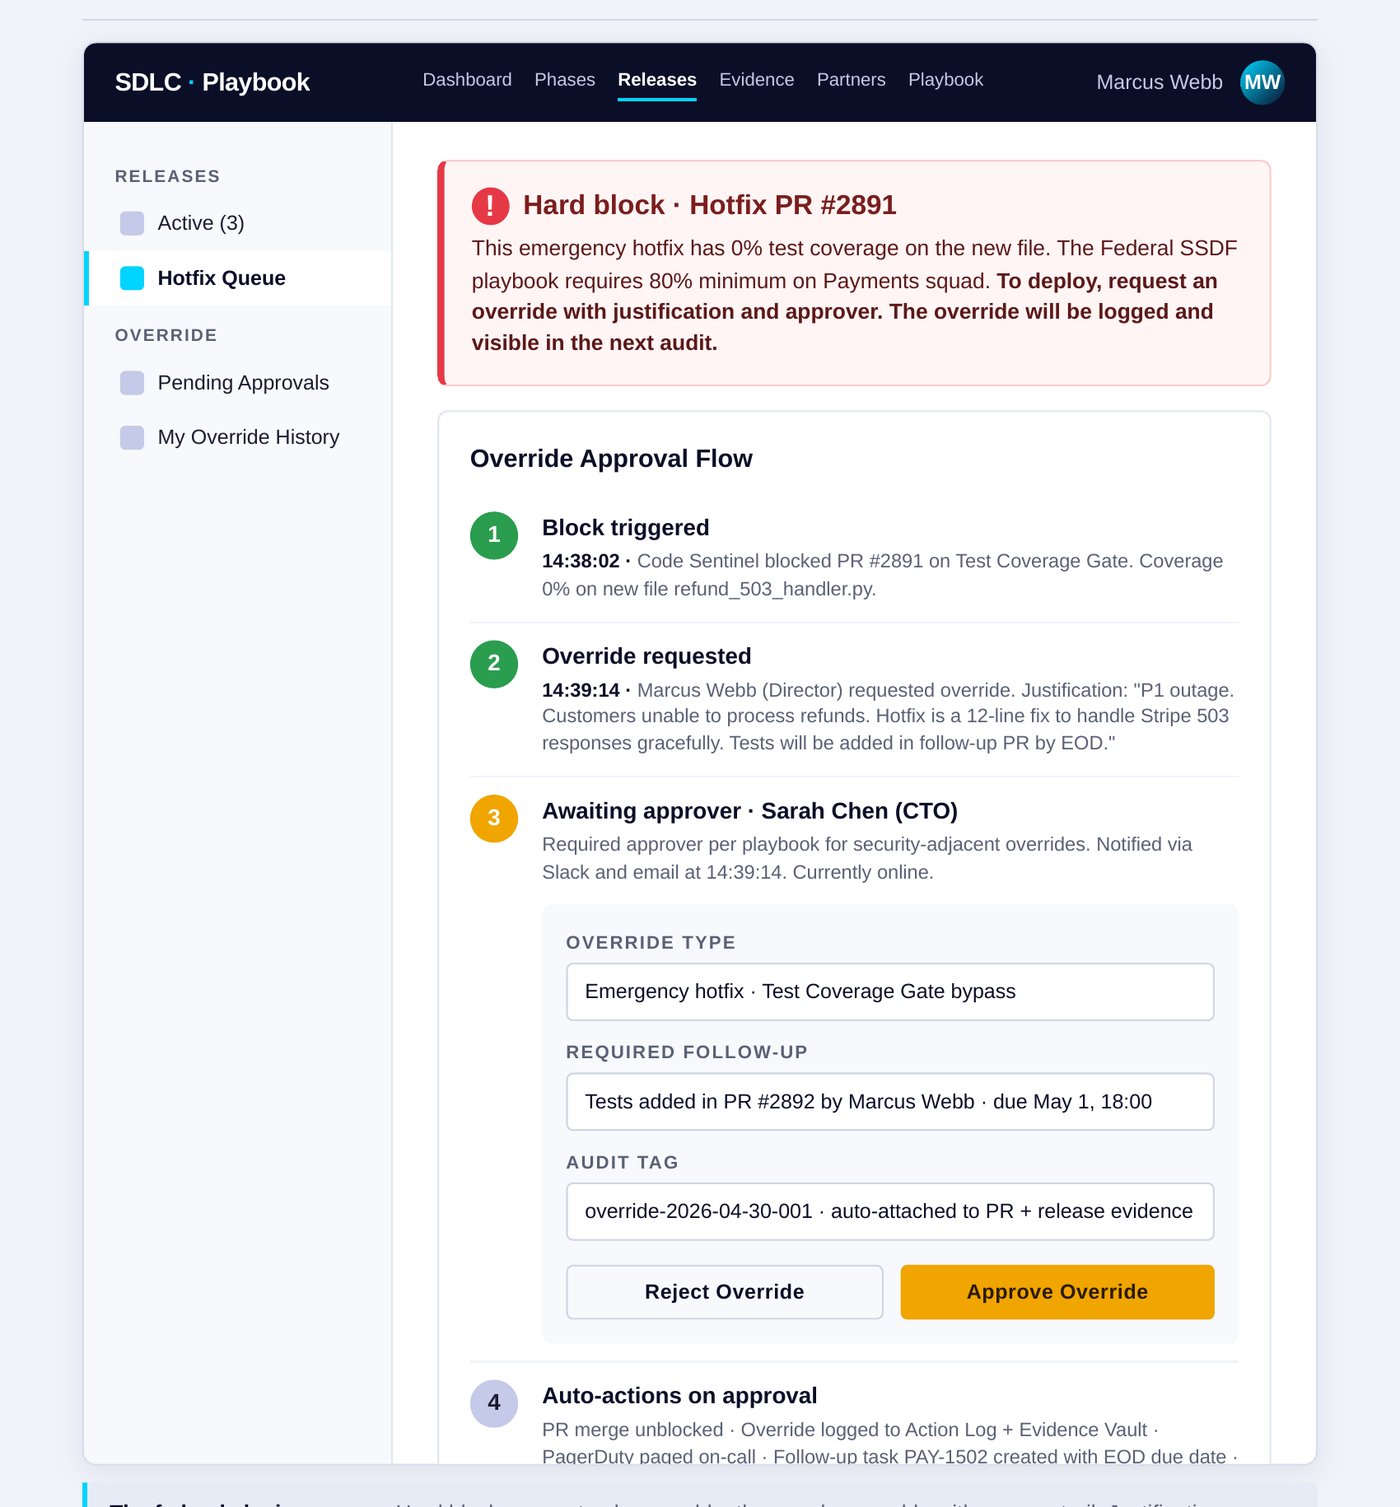
Override with paper trail
Hard blocks bend without breaking. Justification, approver routing, follow-up task, audit tag. The auditor sees the override, the reason, and the resolution.
Documentation that writes itself
Documentation agents work in concert. Compliance docs update continuously against the live evidence vault. Release notes auto-draft from sprint contents.
Why the AI outputs don’t sound generic.
Two architectural decisions that make the difference between AI that “parachutes in” and AI that knows your product.
Per-tenant knowledge layer.
Project Brain captures what your software actually is — project profile, tech stack, components, domain vocabulary, prior architecture documents — and injects that context into every AI agent call.
The result: SSPs that read like your team wrote them. Release notes that use your customer-facing product names. Coach explanations grounded in your codebase. AI outputs you don’t have to extensively rewrite.
Scrum, Kanban, Waterfall built-in.
The product fits the customer, not the other way around. Scrum tenants see Sprints and Stories. Kanban tenants see WIP limits and continuous flow. Waterfall tenants see Phases and Phase Approval gates.
Same architecture, methodology-aware vocabulary. Engineering Director dashboards use the team’s actual language. Custom methodologies available in Enterprise tier post-MVP.
Plus: Smart Onboarding imports pre-existing evidence (SSPs, audit findings, runbooks) tagged “imported, not generated” so auditors see the boundary clearly. Two years of compliance work isn’t thrown away.
AI agents SDLC roster.
Three classes. Shipping today, then a phased roadmap.
Phased rollout from MVP through v2.0. Shipping today: enforcement (6 PR gates run by Code Sentinel, 6 release gates run by Release Gatekeeper, plus Role Accountability and Requirements Auditor), authoring (Requirements Author, QA Strategist, Discovery Synthesizer, ADR Author), and documentation (Release Composer, Compliance Scribe). v1.2 adds four sprint-ceremony and compliance agents. v1.3 adds Design Review Coach. v2.0 deepens existing agents with code-level capabilities.
v2.0 deepens existing agents with code-level capabilities: architectural drift detection, missing-test detection, API contract verification. Twenty distinct capabilities across thirteen agents at v2.0.
Five shipped integrations.
Six on the roadmap.
SDLC Playbook takes real action in real systems. Read-only versus write actions are clearly distinguished, and every action is logged. Authoring agents only write to Jira and ADO Boards after explicit human approval.
GitHub
Block merges via status checks. PR comments. Sub-PRs. Release tags.
Azure DevOps
Block pipeline stages. Update story status. Attach evidence. Authoring writes for stories.
Slack
Broadcast notifications to a connected channel, and chat approvals captured as control-mapped evidence. Threads, weekly briefs, and standup summaries coming soon.
Microsoft Teams
Same action surface as Slack: notifications out, and chat approvals captured as control-mapped evidence. Commercial cloud.
Jira
Refuse story closure. Audit comments. Block sprint close. Authoring writes for stories with mandatory human approval.
SonarQube
Reads SonarQube results from your CI artifacts today; direct connector on the roadmap.
Snyk
Reads Snyk results from your CI artifacts today; scan triggering and PR blocking on the roadmap.
PagerDuty
Planned: Page on-call when production gate is overridden.
ServiceNow
Planned: Auto-create change tickets for production deploys. Evidence pre-attached.
DocuSign
Planned: Capture signoffs as legally-binding signatures for audit and compliance evidence.
GitLab
Same action surface as GitHub. Earned when first GitLab customer signs.
Need another?
Tell us in the design partner intake.
Governance capabilities live today.
Built and deployed ahead of the public spec. Each one is on the product now; scope is stated exactly.
Governance Drift Detection
Continuously reconciles the governance you declared against the execution we observe. Is the process you documented the process you actually run? Every control reports one of three states, CONFIRMED, OBSERVED_ONLY, or NOT_OBSERVED_IN_WINDOW, so a gap is never hidden behind a green check.
Risk-tiered governance
Required evidence depth scales with the risk of the change, from blast radius and change type. Low-risk changes move fast; high-risk changes carry more proof.
Tamper-evident evidence with verify
Every evidence item carries a canonical-JSON SHA-256. A verify endpoint confirms the item has not been altered since capture.
Release Approver role and deploy gating
Deny-by-default separation of duties on release sign-off. Nobody approves their own release, and the deploy gate stays closed until a Release Approver signs.
Remediation loop
File a finding to your work-item tracker in one click. The finding, the ticket, and the fix stay linked as evidence.
Cross-framework mapping
One finding lights up every regime the control belongs to, so a single fix updates posture across SSDF, NIST 800-171, and SOC 2 at once.
Chat approval as evidence (Slack and Teams)
A human approval or sign-off made in Slack or Microsoft Teams is captured at the moment it happens as tamper-evident, control-mapped evidence. Other tools notify out; we capture the governance decision in chat. Commercial cloud today. Mapping to SSDF PW.8.2 is partial.
Acceptance Verifier (API criteria)
On a real backlog story, the Acceptance Verifier compiles one acceptance criterion from the story text, never from a proposed test case, into a deterministic HTTP check with no model involved, runs it against the deployed build, and records the result as tamper-evident evidence carrying the build SHA and a truthful, deterministic independence record, then writes a comment back to the story. For a Given/When/Then criterion it executes the Then clause; the Given is a liveness-only precondition, assumed, not independently established. Criteria it cannot test, including UI and stateful ones, are marked NOT_TESTABLE and never passed. It produces evidence, never a status change.
AI agents SDLC questions, answered.
What are the three classes of agents?
Enforcement agents verify human work meets your playbook (Code Sentinel, Release Gatekeeper, Role Accountability, Requirements Auditor, Compliance Auditor (v1.2, roadmap)). Authoring agents draft SDLC artifacts that humans review and approve (Requirements Author, QA Strategist, Discovery Synthesizer, ADR Author, plus four more on the v1.2 / v1.3 roadmap). Documentation agents continuously produce versioned deliverables (Release Composer, Compliance Scribe). Each class has a different execution pattern and different infrastructure needs.
How many agents ship at MVP?
Shipping today: enforcement (6 PR gates run by Code Sentinel, 6 release gates run by Release Gatekeeper, plus Role Accountability and Requirements Auditor), authoring (Requirements Author, QA Strategist, Discovery Synthesizer, ADR Author), and documentation (Release Composer, Compliance Scribe). v1.2 (months 4-6) adds Standup Synthesizer, Retrospective Coach, Sprint Planner, Compliance Auditor. v1.3 (months 7-9) adds Design Review Coach. v2.0 (months 10-12) deepens existing agents with code-level capabilities. Total of thirteen distinct agents at v2.0.
How do authoring agents stay safe with write access to Jira and Azure DevOps?
Three guardrails. First, every write requires explicit human approval — no agent silently commits to your work item system. Second, every write carries a WriteContext naming the approving user and originating session, enforced at the interface level. Third, authoring agents are field-scoped: they can write Title, Description, Acceptance Criteria, and Test Plan References, but cannot modify Status, Assignee, or Priority — those stay under your team’s workflow control. Customer admins can disable write capability per integration in Settings.
What is Project Brain?
Project Brain is a per-tenant knowledge layer that captures what your software actually is — project profile, tech stack, components, domain vocabulary, prior architecture documents — and injects that context into every AI agent call. The result: SSPs that read like your team wrote them, release notes that use your customer-facing product names, and Coach explanations grounded in your codebase. Without this, AI outputs feel generic and require heavy rewriting.
Does it work with Scrum, Kanban, and Waterfall teams?
Yes. The Methodology Engine ships three built-in methodologies. Scrum tenants see Sprints and Stories. Kanban tenants see WIP limits and continuous flow. Waterfall tenants see Phases and Phase Approval gates. Same architecture, methodology-aware vocabulary. Custom methodologies are available in Enterprise tier post-MVP.
Can I import pre-existing evidence?
Yes. Smart Onboarding accepts existing SSPs, audit findings, threat models, runbooks via PDF, Word, Markdown, or ZIP upload. Imported documents are tagged “imported, not generated” so auditors see the boundary clearly. Your prior compliance work becomes input to your next audit, not a competitor to ignore. Every audit export includes a Coverage Statement distinguishing observed gate evaluations from imported historical records.
How does the Override workflow keep audits clean?
Hard blocks bend without breaking. An override requires justification, an approver, a follow-up remediation task, and an audit tag. The override is logged to both the Action Log and the tamper-evident Evidence Vault. The auditor sees the override, the reason, the approver, and the resolution — nothing hidden.
See it in your stack.
Request a 30-minute demo. We’ll show you what the product looks like running against your repo, your tracker, your team.